The challenge
This started as a question rather than a requirement: could custom software make SIEM log analysis genuinely useful? The proof of concept answered that quickly, and the scope grew from there.
What we built
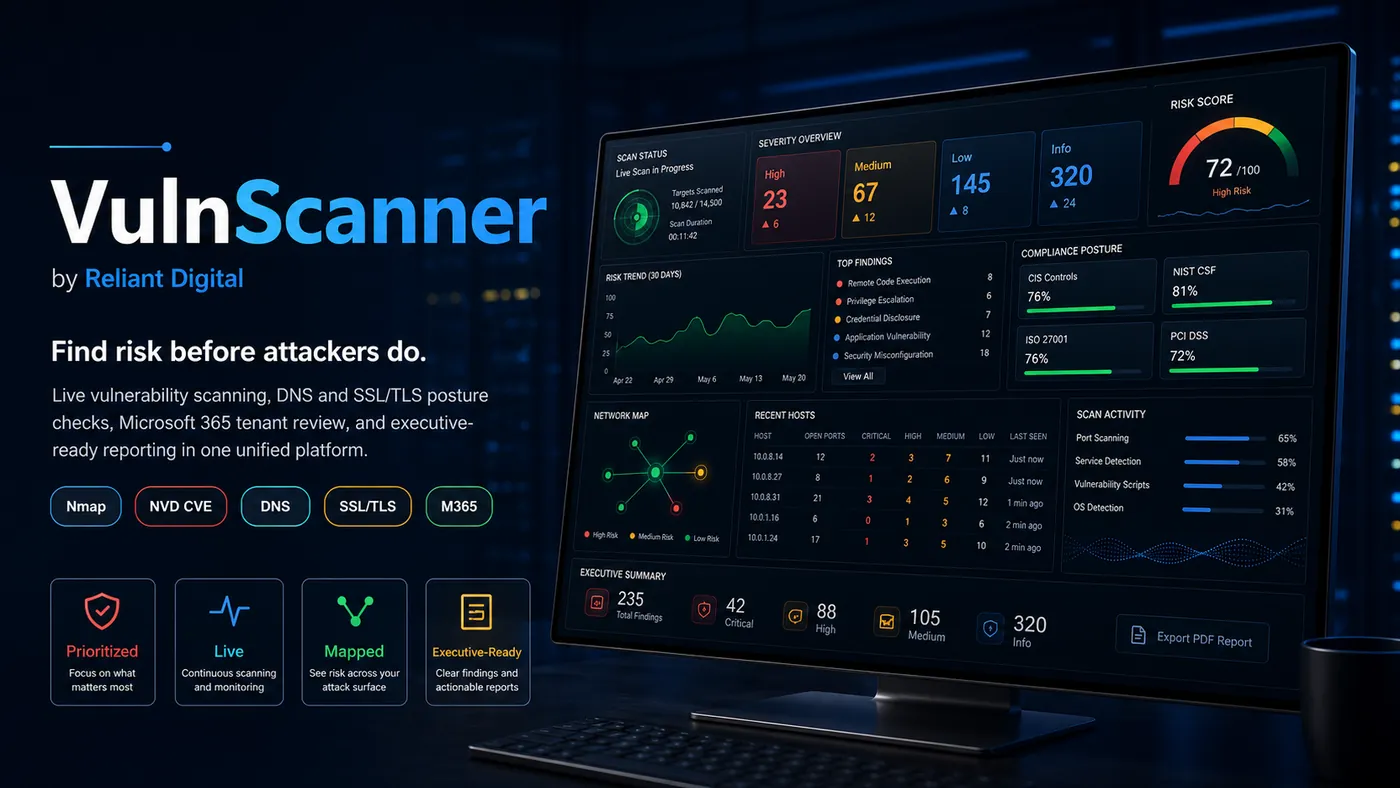
VulnScanner became a robust penetration-testing and vulnerability scanning tool with cloud, LAN, and WAN scanning capabilities. It produces clear, client-ready reports covering severity, compliance posture, network mapping, and scan activity.
A private AI integration keeps findings freshly reviewed and notifies the SOC team when something needs attention. The AI layer is optional — the platform works fully with or without it.
Capabilities
- Cloud, LAN, and WAN vulnerability scanning
- DNS and SSL/TLS posture checks
- Microsoft 365 tenant review
- Network mapping and asset discovery
- Executive-ready reporting
- Private AI analysis and SOC notifications (optional)
The outcome
Another proof of concept that ended up in production. About a month from first idea to deployment, VulnScanner now delivers top-tier assessment reports for the client and runs continuously with or without its AI layer.